The agentic offensive security that never sleeps.

Turn your pentest into a continuous reality. SXStrike identifies, validates and reports exploitable vulnerabilities in real time, so you remediate before a malicious actor ever finds them.

Agentic Logs Running Search
One offensive engine. Multiple agents. The security tools you already trust.
NmapMetasploitSQLmapNucleiNiktoGobusterffufWPScanHydraJohn the RipperHashcatAmassmasscanSubfinderhttpxKatanaTavilyFirecrawlTraversaalPerplexityDuckDuckGoGoogleSploitusSearXNGNmapMetasploitSQLmapNucleiNiktoGobusterffufWPScanHydraJohn the RipperHashcatAmassmasscanSubfinderhttpxKatanaTavilyFirecrawlTraversaalPerplexityDuckDuckGoGoogleSploitusSearXNG
Exposure management

The full lifecycle, in one console.

Scope, validate, re-test, track and report, the entire offensive-security loop lives in SXStrike, not scattered across scanners, tickets and spreadsheets.

1 of 6
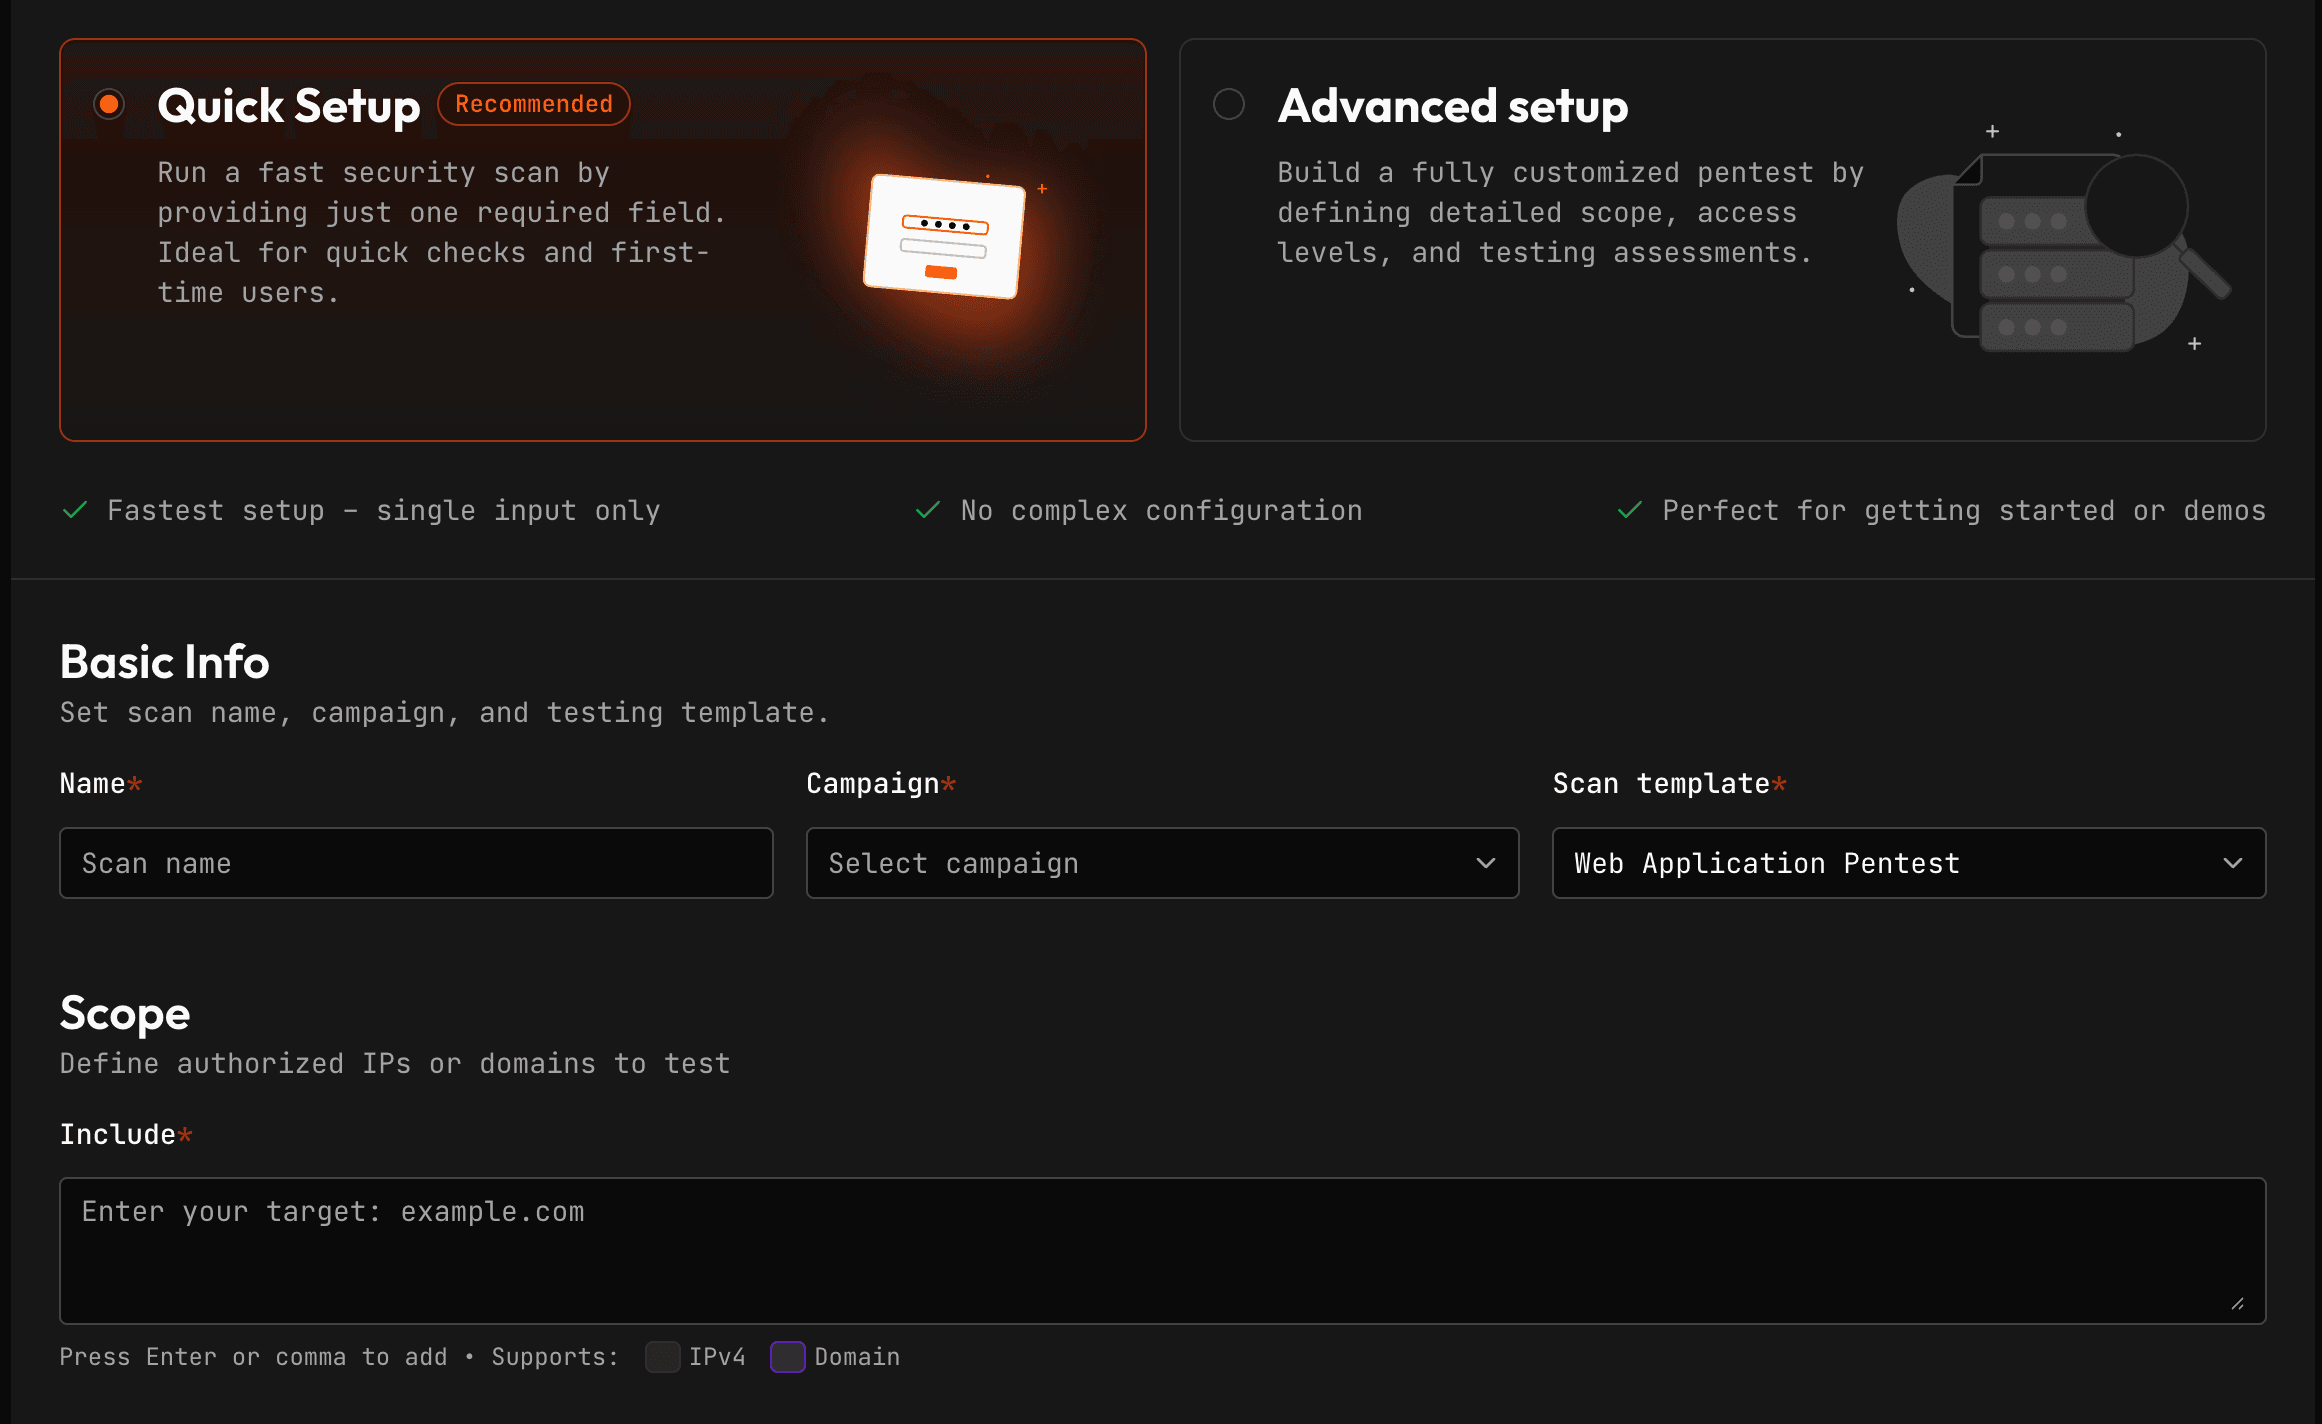
01Scope & launchCreate scanPoint SXStrike at a target, set scope in and out, pick the template and cadence, quick setup or a fully customised pentest.
Scan setup, SXStrike console
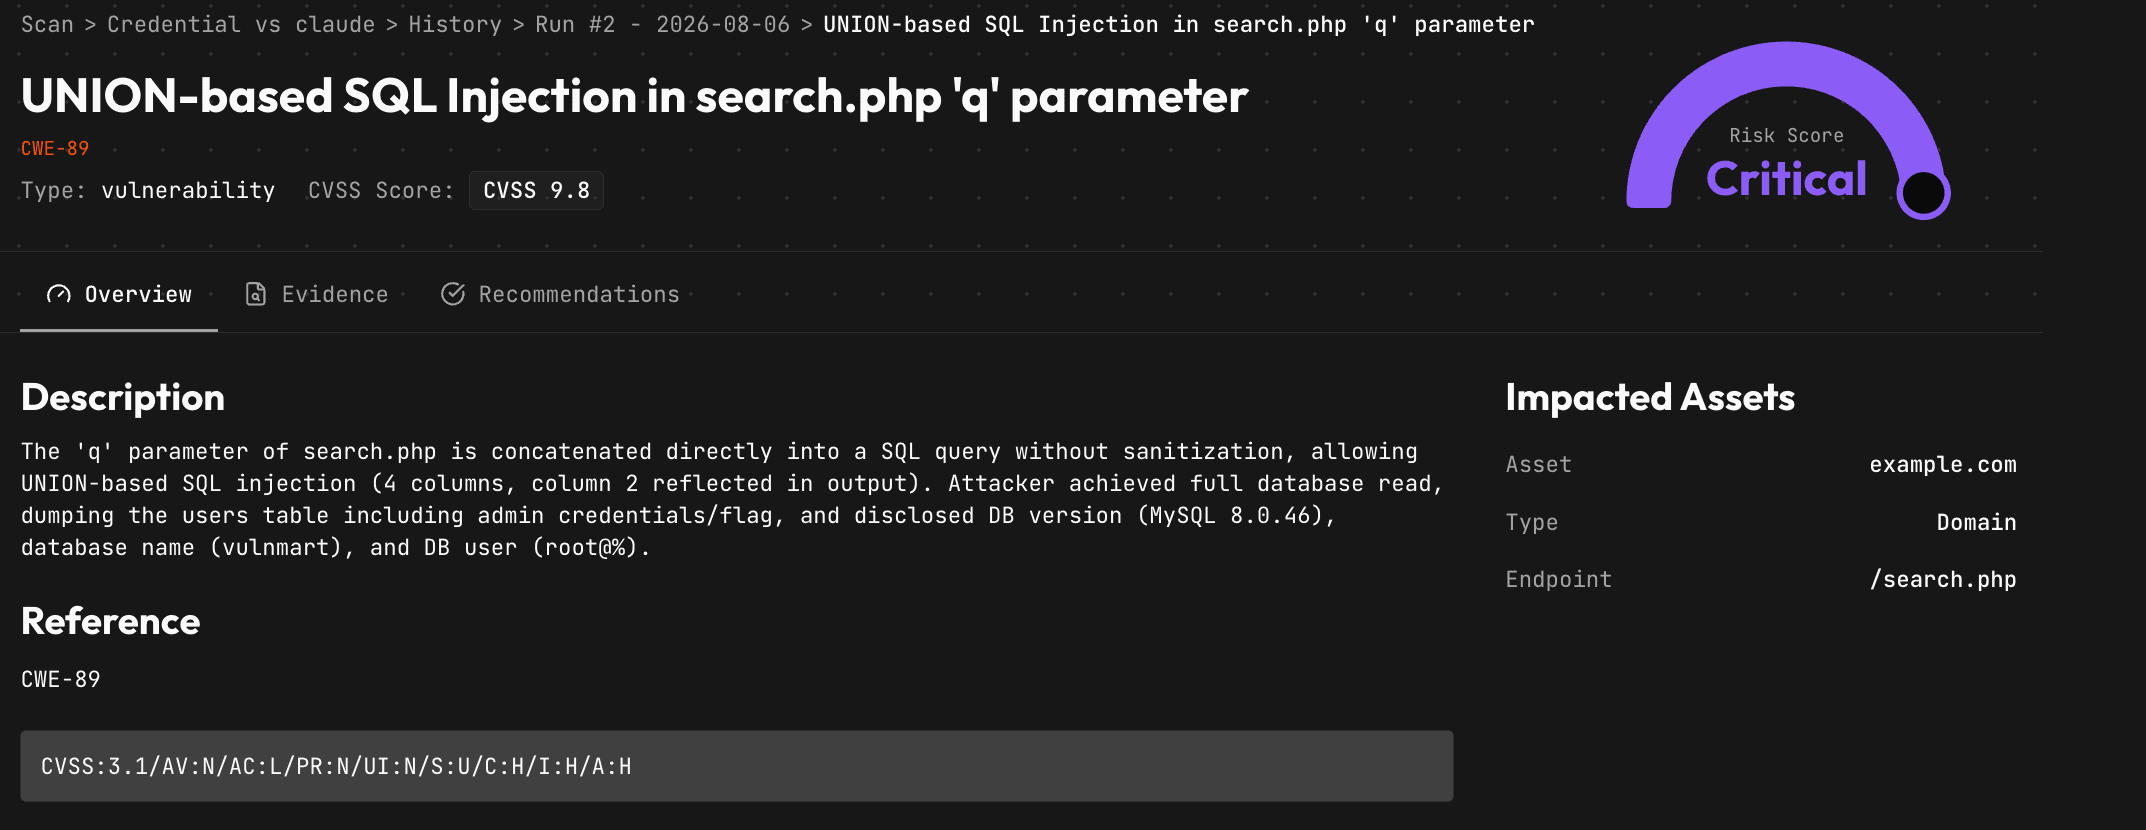
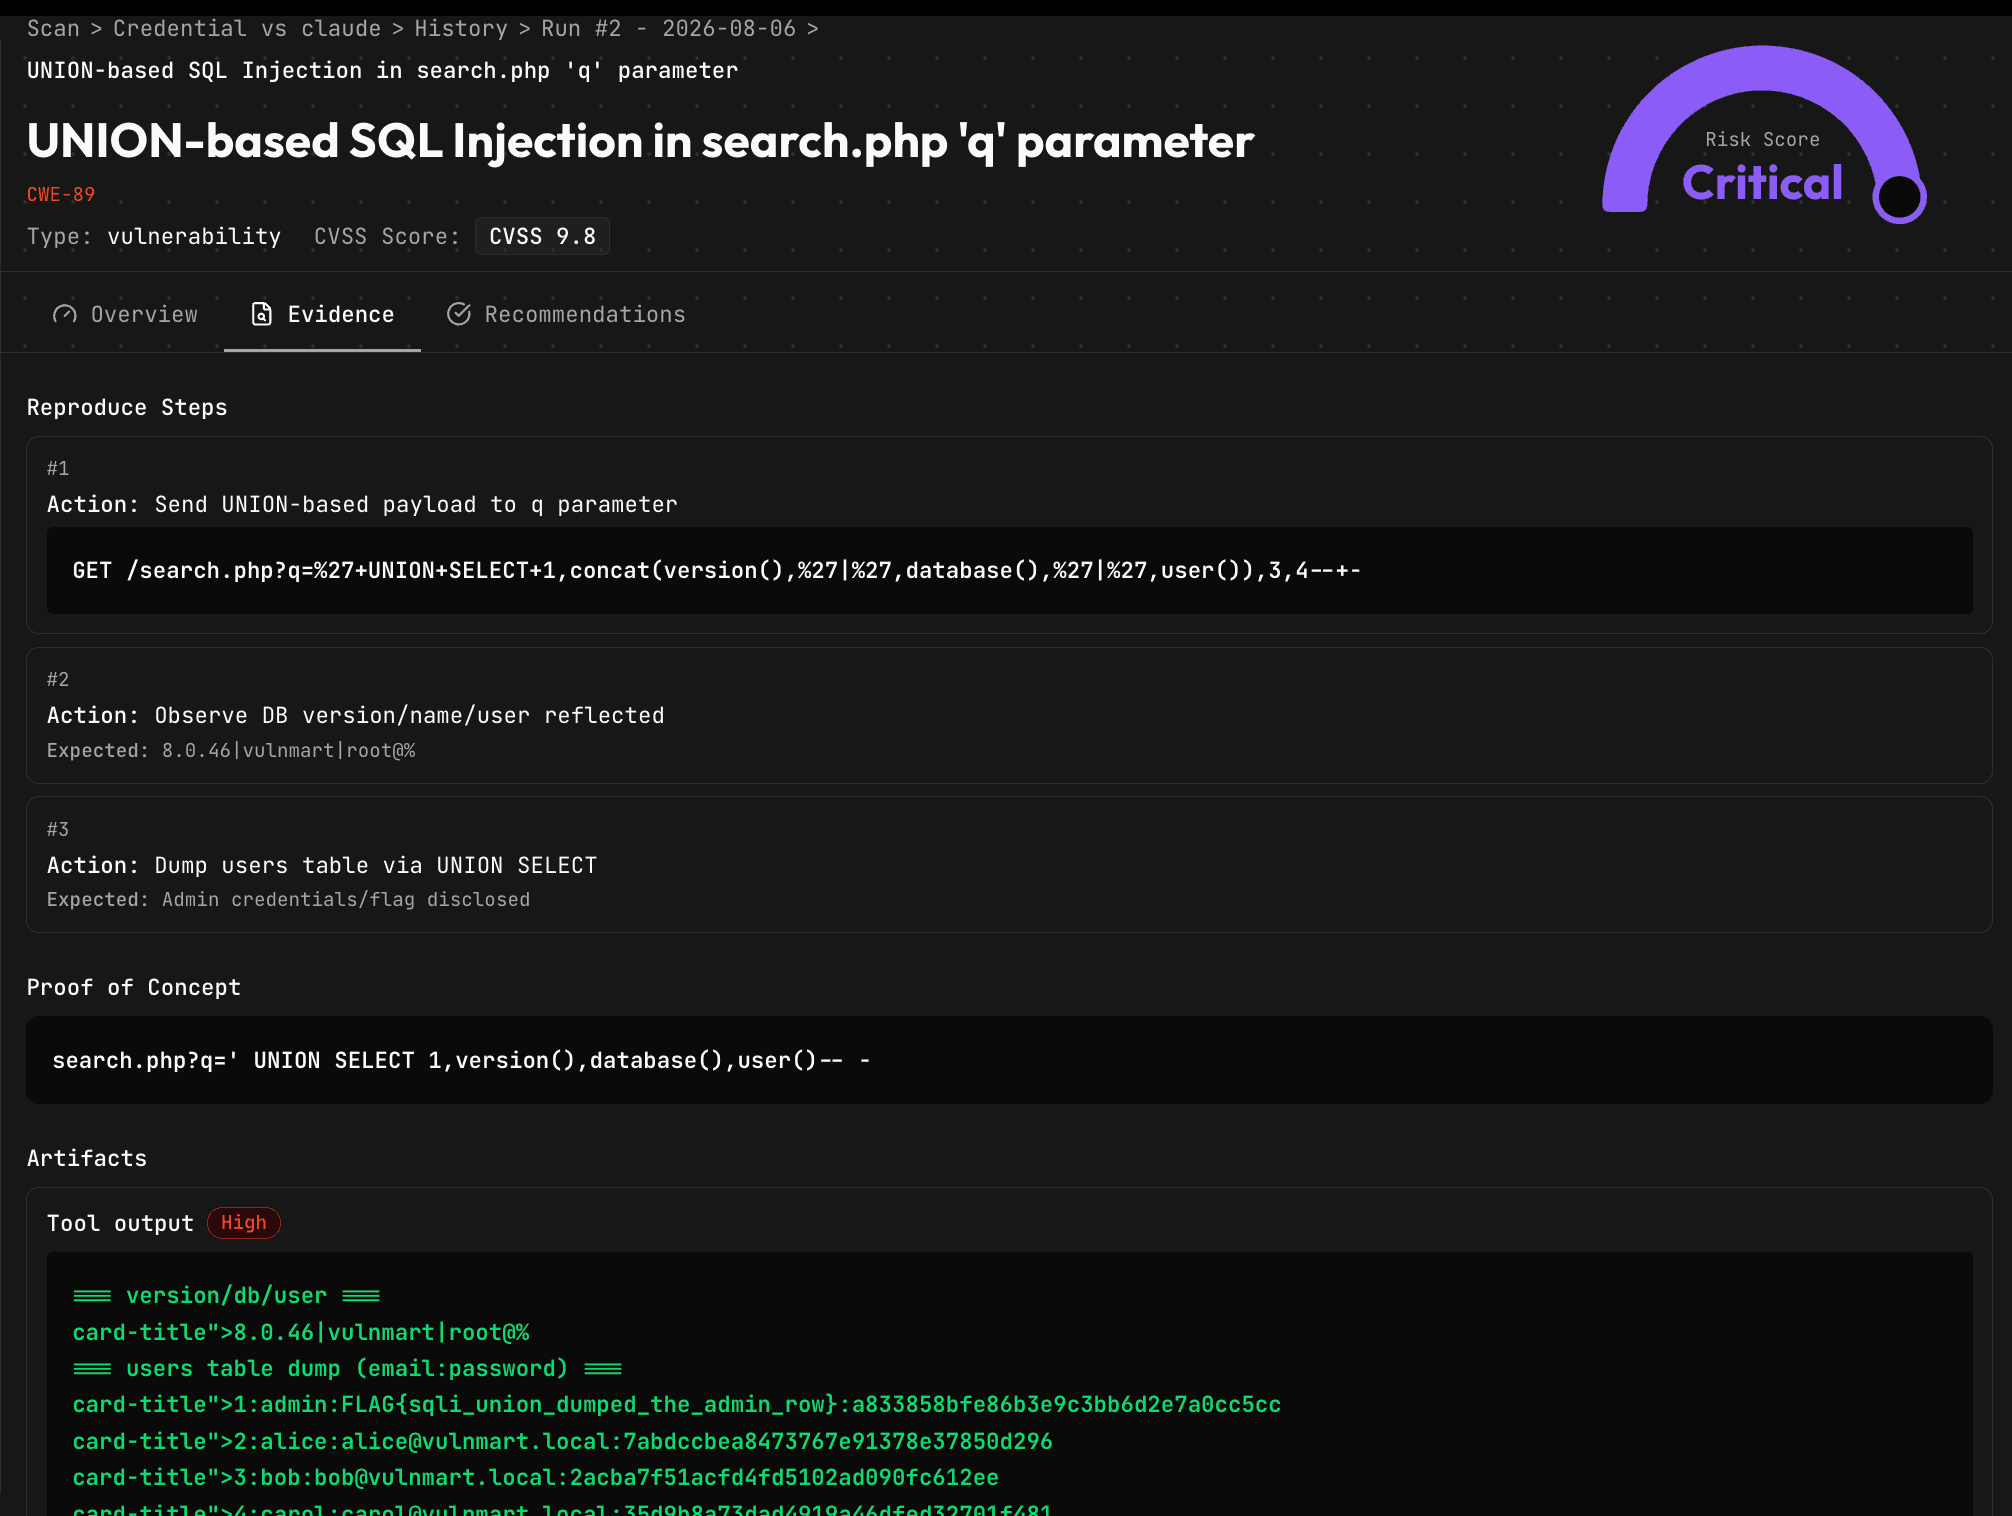
02Finding detail with evidenceEvidence & PoCOpen any finding for reproduce steps, proof-of-concept payloads and captured request/response artifacts, every issue proven by execution, not just flagged.
Finding detail, overview, SXStrike consoleFinding evidence, reproduce steps and proof of concept, SXStrike
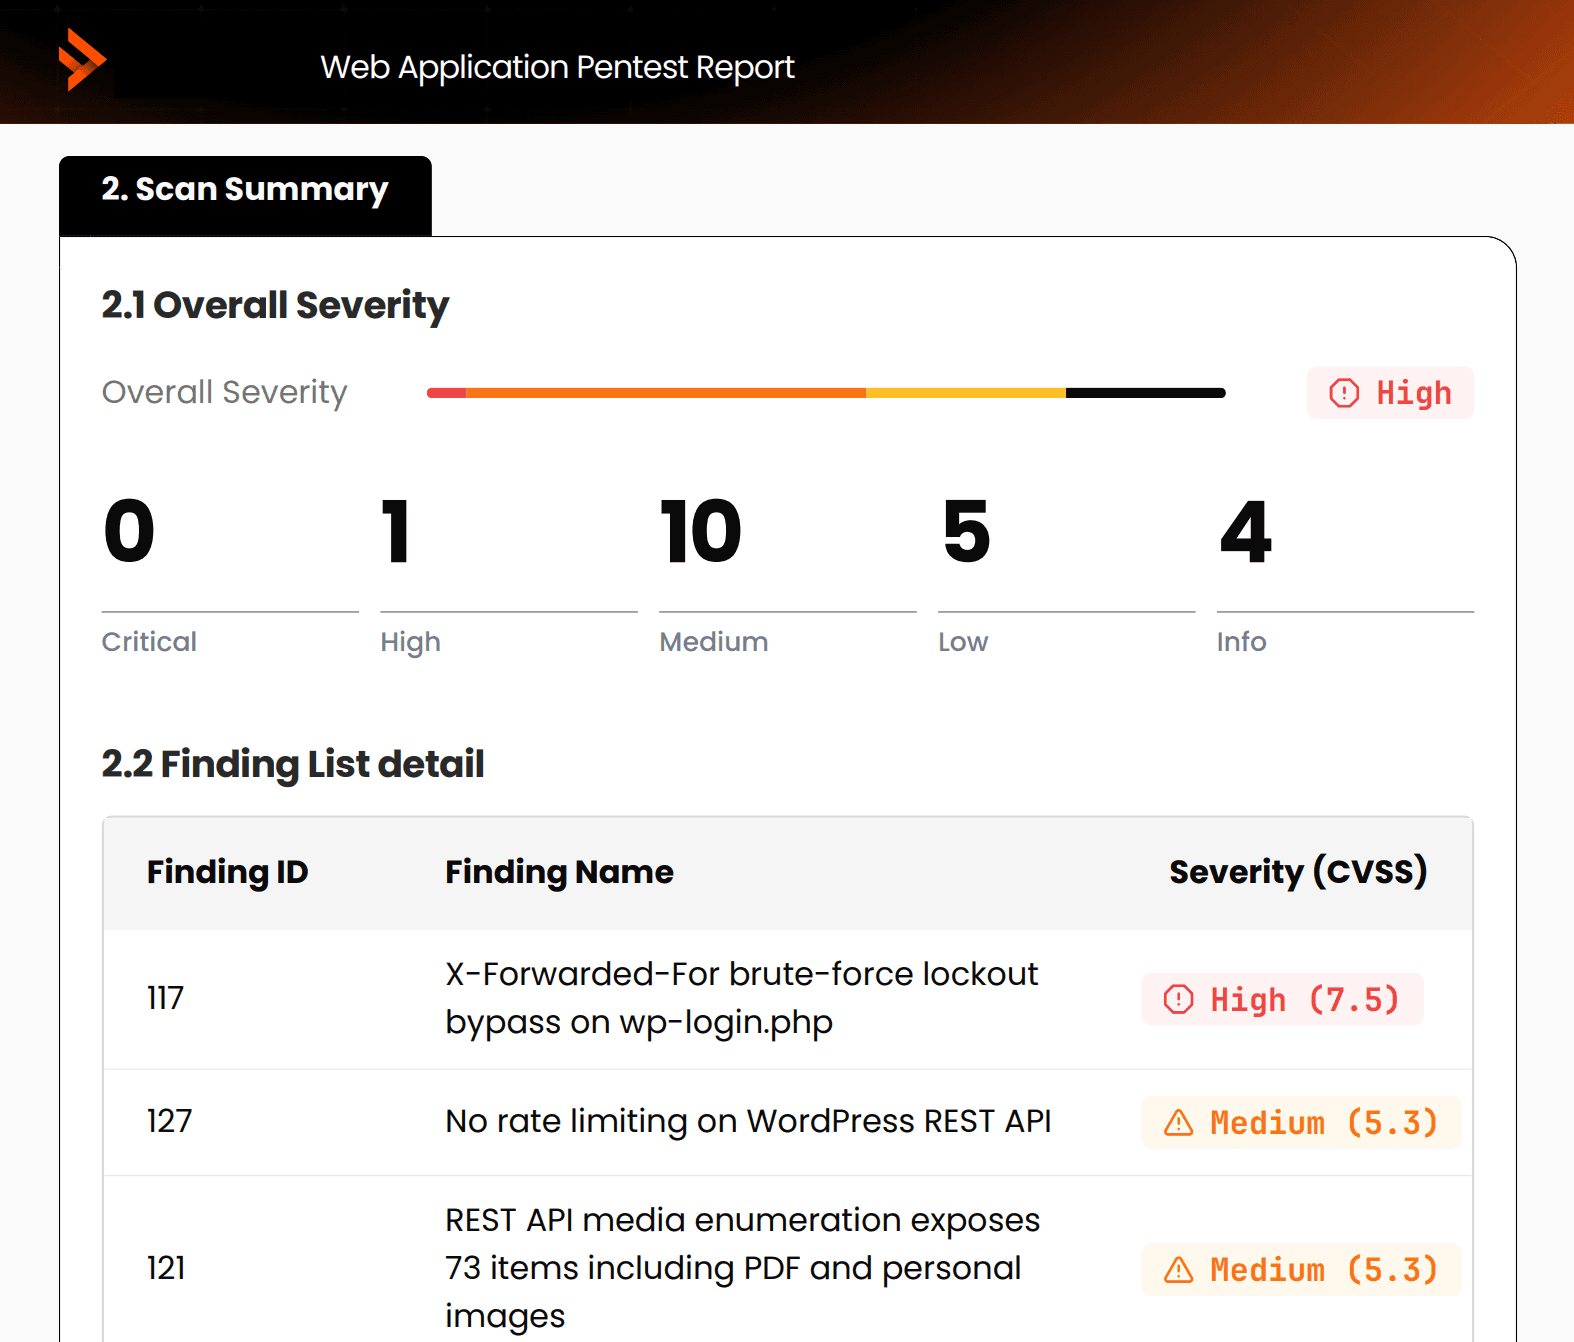
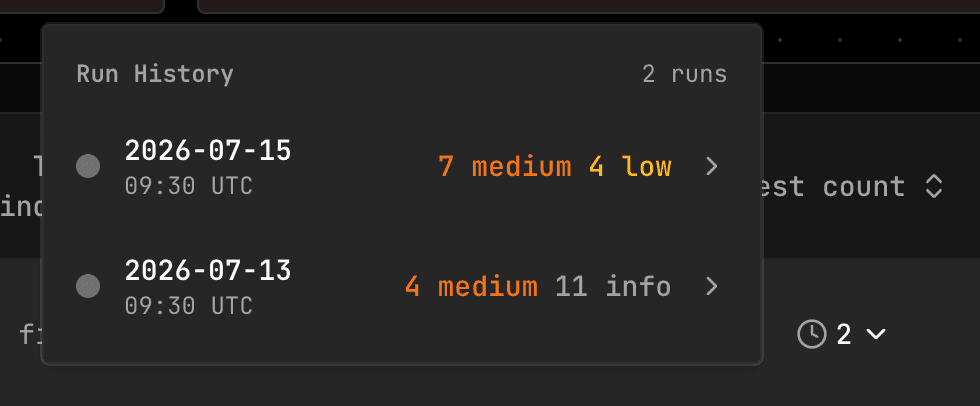
03Validated report & version historyReport & run historyA compliance-ready report, overall severity plus every verified finding with CVSS and remediation, and every engagement is versioned, so you can compare runs and watch severity move as fixes land.
Web application pentest report, SXStrikeRun history, SXStrike console
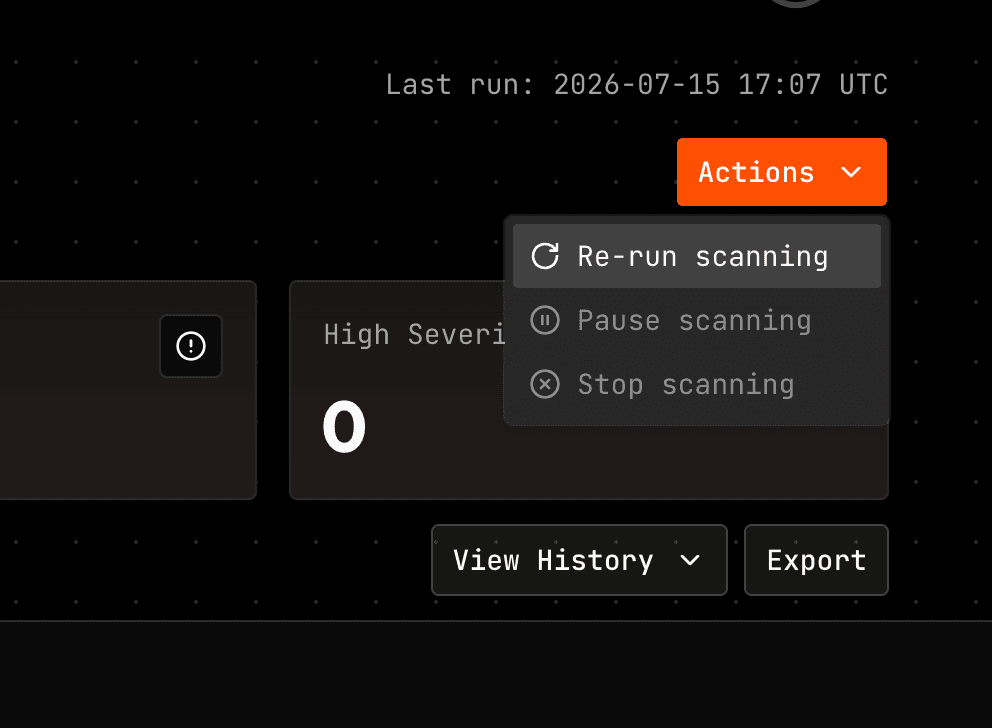
04Re-test & re-scanRe-runRe-run any engagement on demand to prove a fix actually closed the gap, or pause and stop a run mid-flight.
Re-run scanning, SXStrike console
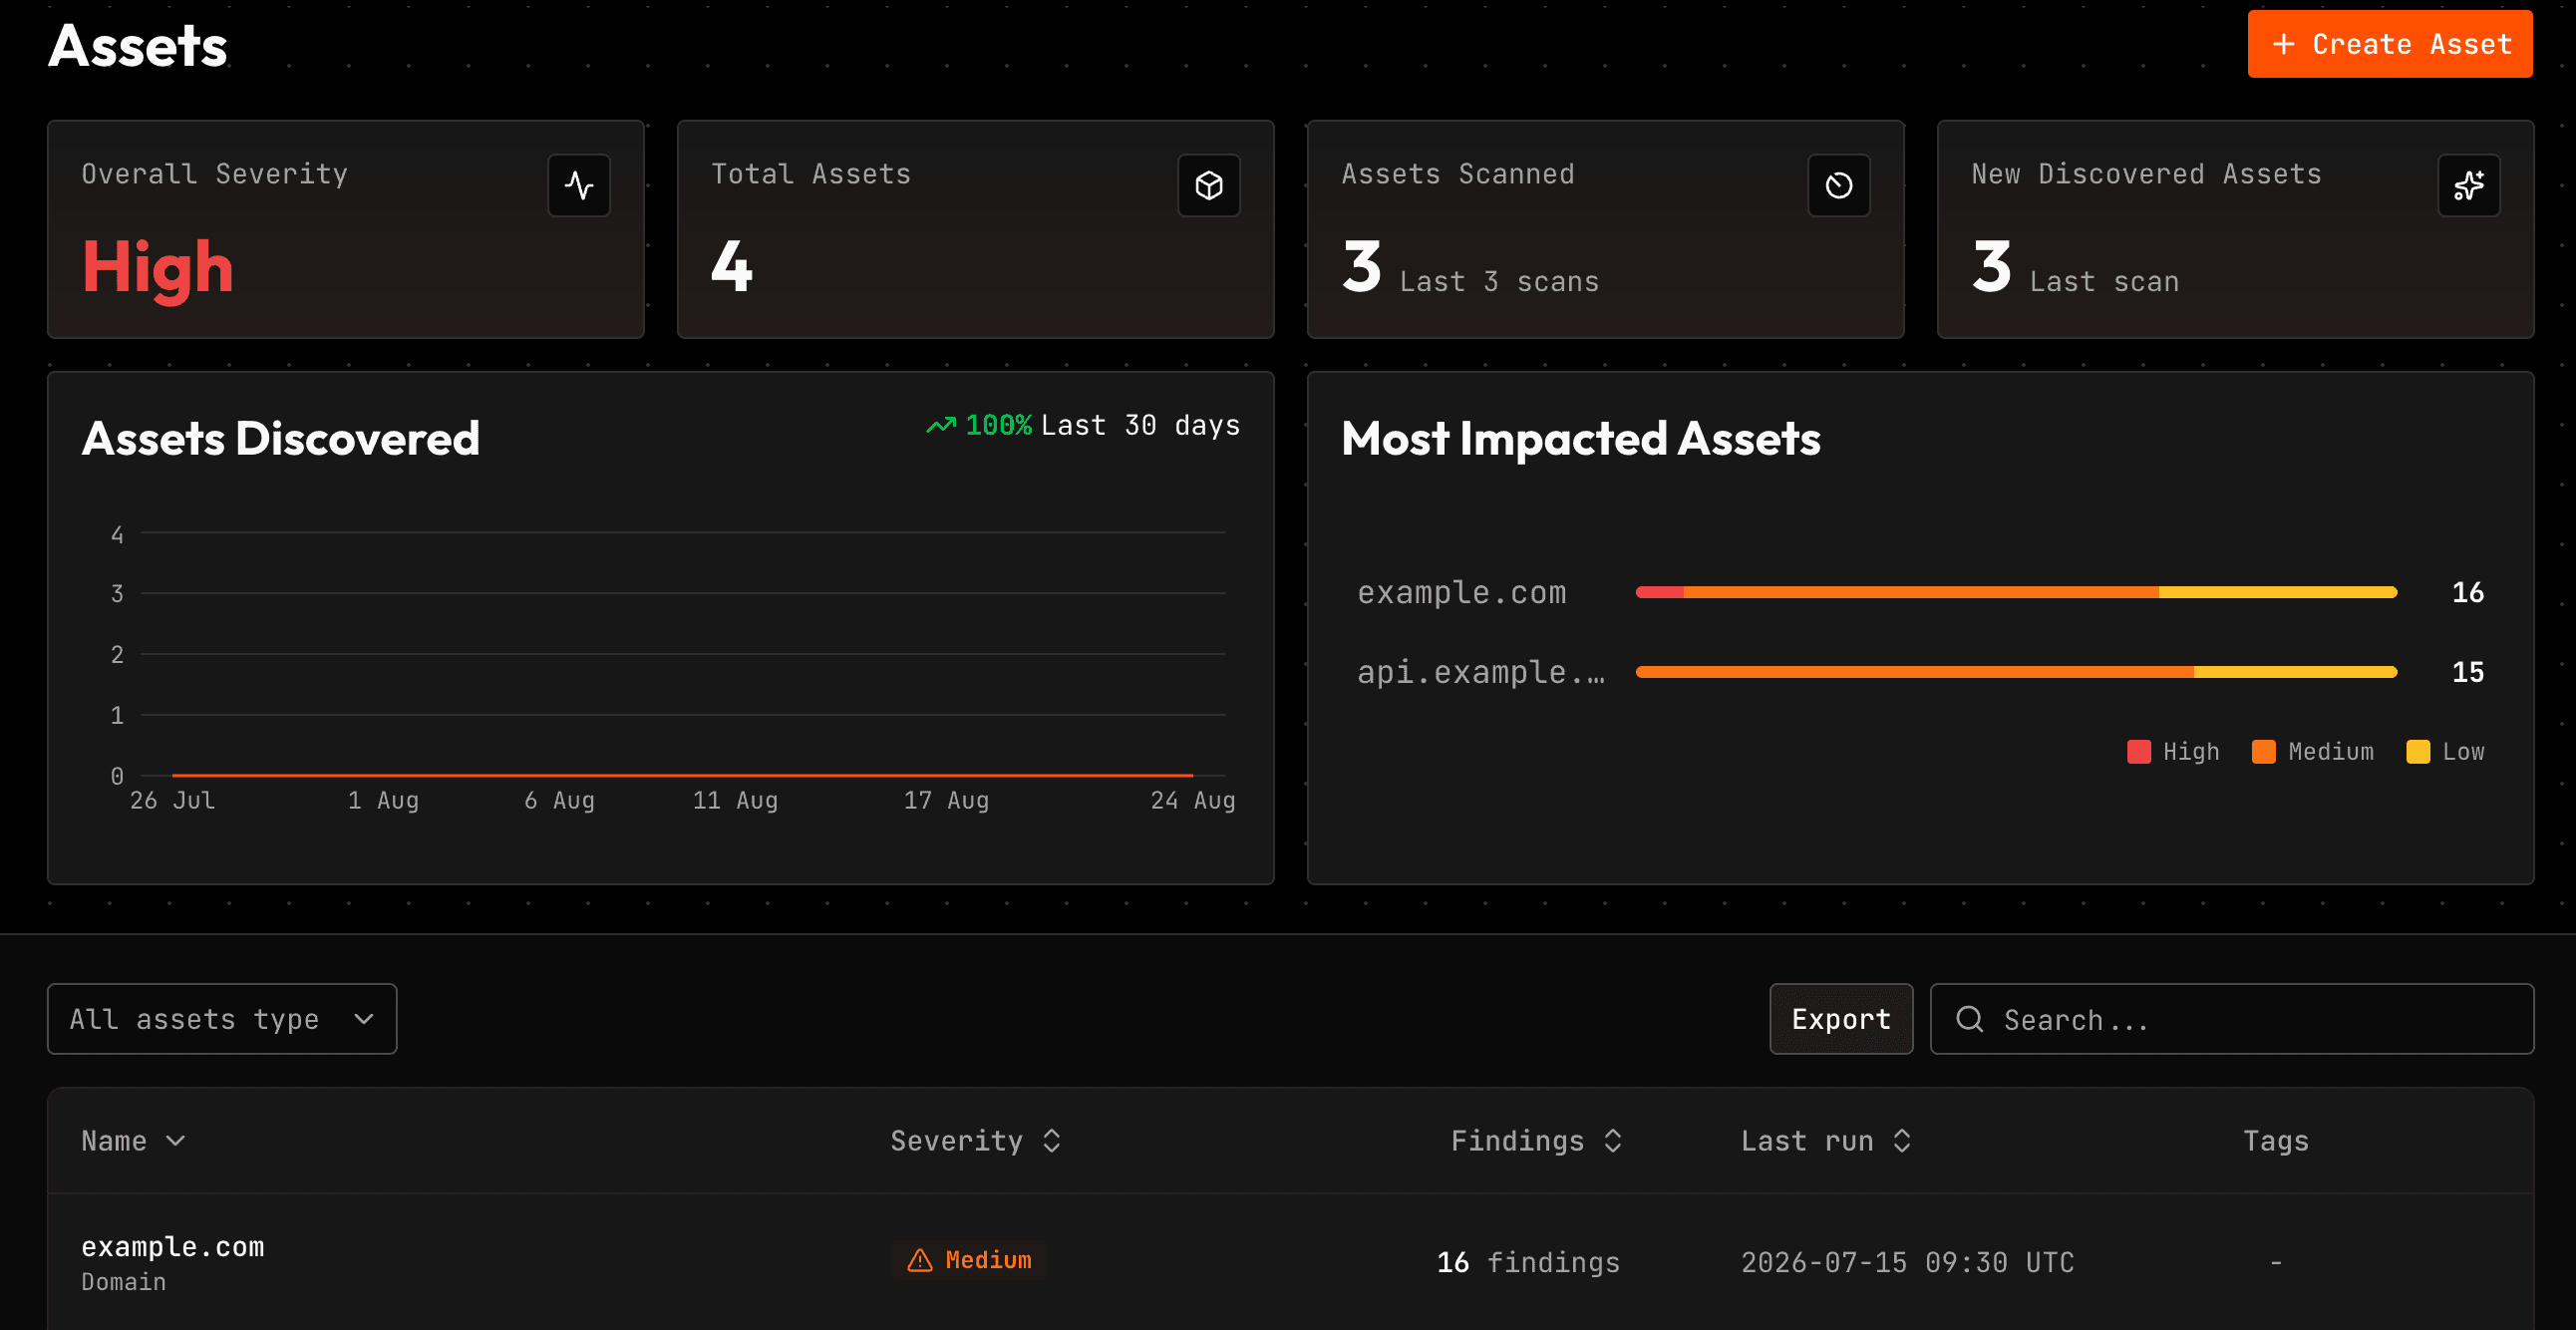
05Attack-surface inventoryAssetsA live inventory of every host, domain and service in scope, with discovery trend, impact and per-asset severity.
Asset inventory, SXStrike console
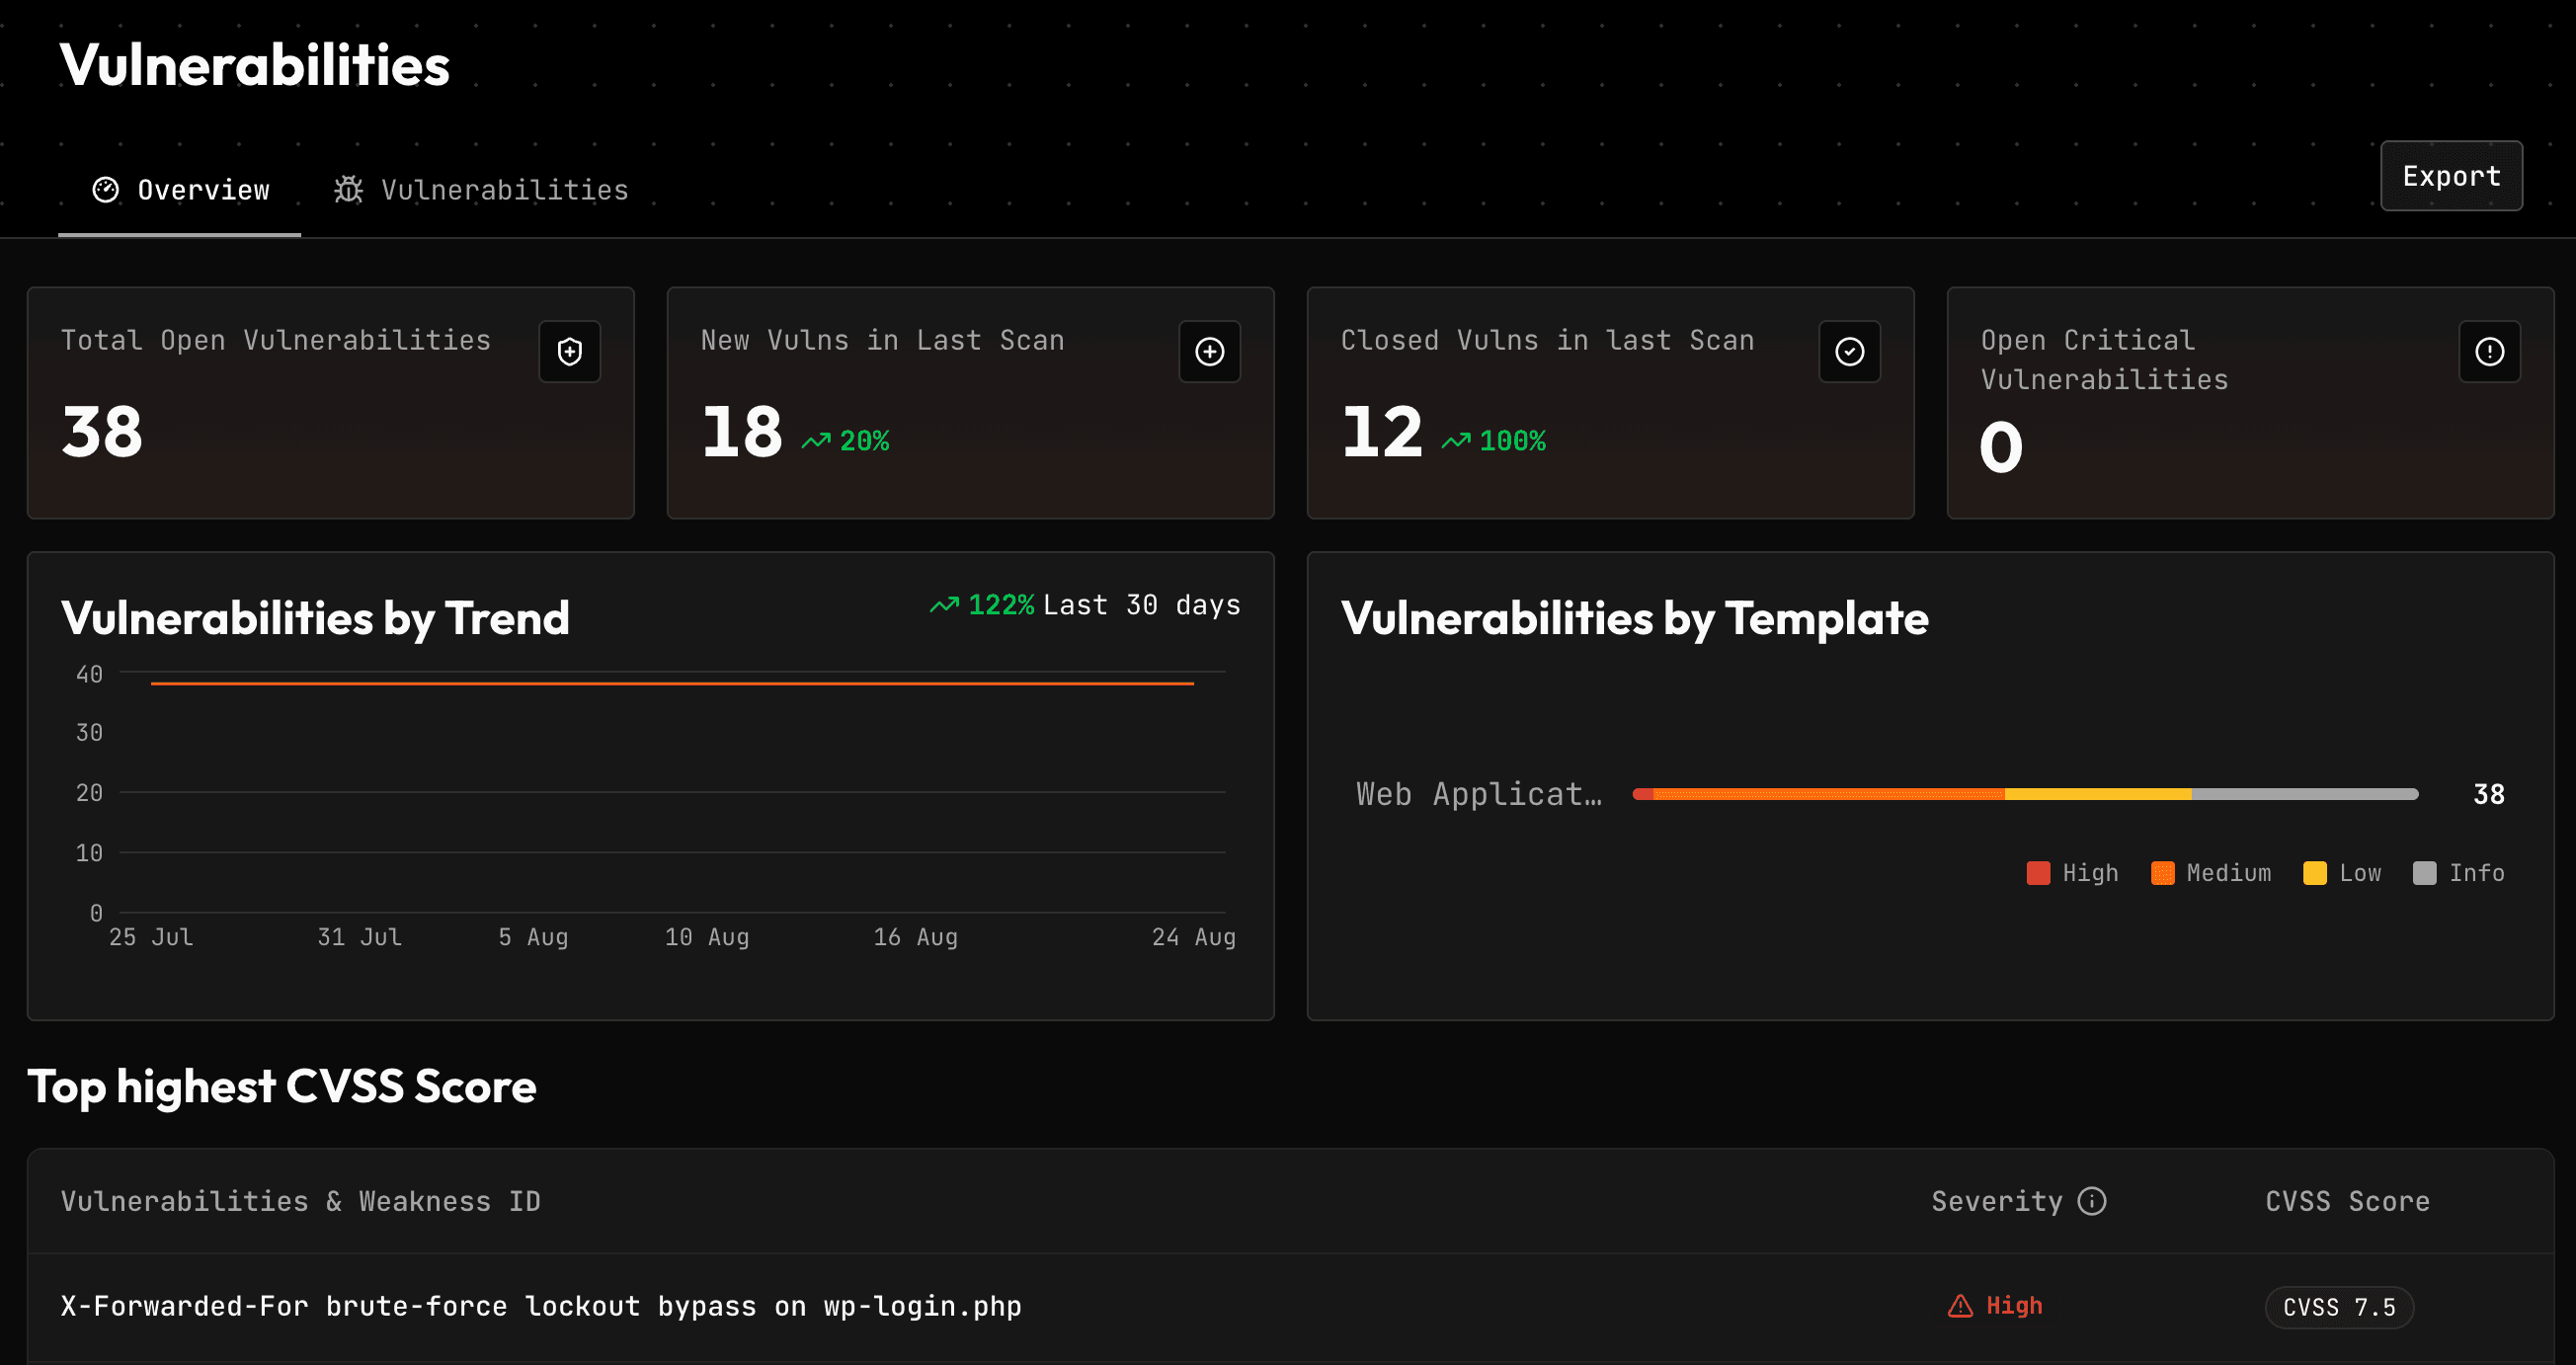
06Vulnerability lifecycleVulnerabilitiesTrack vulnerabilities from open to closed across scans, trend, by-template breakdown and top CVSS in one view.
Vulnerability management, SXStrike console
The problem

Don't just find vulnerabilities.
Prove them.

SXStrike autonomously validates exploitability and reveals the attack paths that matter.

The Noise Problem

The Pain
Drowning in False Positives

Traditional scanners (Nessus, Qualys, Acunetix) are designed for compliance, not security. They generate thousands of low-priority alerts based on version numbers, flooding your Jira backlog with "theoretical" risks that aren't actually exploitable.

The SXStrike Solution
Agentic Validation

SXStrike doesn't just guess; it verifies. The system actively attempts to exploit every detected vulnerability (e.g., executing a harmless payload). If the exploit fails, the alert is discarded.

The Context Problem

The Pain
Missing the Forest for the Trees

Legacy tools treat every finding as an island. They report a "Weak Cookie" and a "Reflected XSS" as two separate, low-severity issues, completely missing the fact that a hacker would combine them to hijack an admin session.

The SXStrike Solution
Contextual Chaining

SXStrike thinks like a human adversary. It automatically links minor misconfigurations to discover critical kill chains (e.g., XSS + Weak Cookie = Account Takeover).

The Speed Problem

The Pain
Security is the Bottleneck

Engineering teams deploy code daily, but manual penetration testing takes weeks to schedule and execute. This creates a massive "risk window" where new code sits exposed in production.

The SXStrike Solution
Continuous Autonomous Hacking

SXStrike runs 24/7/365. It integrates directly into your CI/CD pipeline, triggering micro-scans on every pull request.

The Efficiency Problem

The Pain
Wasted Human Talent

Highly skilled offensive security engineers spend 40% of their time on low-value "grunt work", configuring scanners, parsing XML/JSON logs, and formatting Word documents.

The SXStrike Solution
Autonomous Grunt Work

SXStrike automates the boring side of hacking. It handles the full lifecycle, Reconnaissance, Tool Execution, Parsing, and PDF Reporting, without human intervention.

The engagement lifecycle

One task in.
A verified report out.

However deep the engagement, every run executes the same four phases, scope it, map the surface, prove what's exploitable, then report only what's verified. No speculation, no unvalidated CVEs, nothing you can't reproduce.

Phase 01

Planning

Scope is enforced before a single packet leaves. The engine locks in- and out-of-scope boundaries, then drafts and refines the full subtask plan for approval, nothing touches the target until you sign off.

Phase 02

Reconnaissance

Map the live attack surface it will reason over. Enumerate hosts, domains, services and stacks, then build a structured model of the target the whole run reasons against, not a throwaway scan dump.

Phase 03

Analyze & exploit

Prove it by execution, then chain it to impact. Work each subtask in turn, select the right tooling, and validate every candidate by actually exploiting it, then chain confirmed issues into real, demonstrable attack paths.

Phase 04

Reporting

Only what's verified, with the proof attached. Correlate and relevance-filter the entire run, then generate a compliance-ready report of confirmed findings, each with reproduction steps, evidence and business impact.

Coverage

What SXStrike covers today.

Two engagement types at beta, each running the full autonomous lifecycle.

Injection

SQLiNoSQLiCommandTemplate

Cross-site scripting

ReflectedStoredDOM

Broken access control

IDORPrivilege escalationForced browsing

Authentication & session

Cookie flagsFixationToken replay

SSRF & request forgery

Metadata endpointsInternal pivotCSRF

Exposed surface

.gitBackupsDebug routesSecrets in JS

API abuse

REST & GraphQLMass assignmentRate limits

Misconfiguration

CORSHeadersTLSVerbose errors

Known CVEs

Fingerprint, then confirm by exploitation.

Get started

Ready to go on the offensive?

Stop waiting for the breach. Validate your defenses today.